PhD Researcher · Threat Hunter

I map the I2P darknet and write up threat investigations, case by case.

I’m Joshua Berkoh, a PhD researcher at the University of Cincinnati and a former security engineering intern. I publish network-measurement research on anonymous overlays and CTI reports mapped to MITRE ATT&CK.

2IEEE papers accepted in 2026 (iThings, Smart Data)
1,400I2P eepsites crawled
366,304hyperlinks mapped into a relationship graph
Open dataValidation dataset on IEEE DataPort

Featured Research

Measuring the I2P hidden-service ecosystem
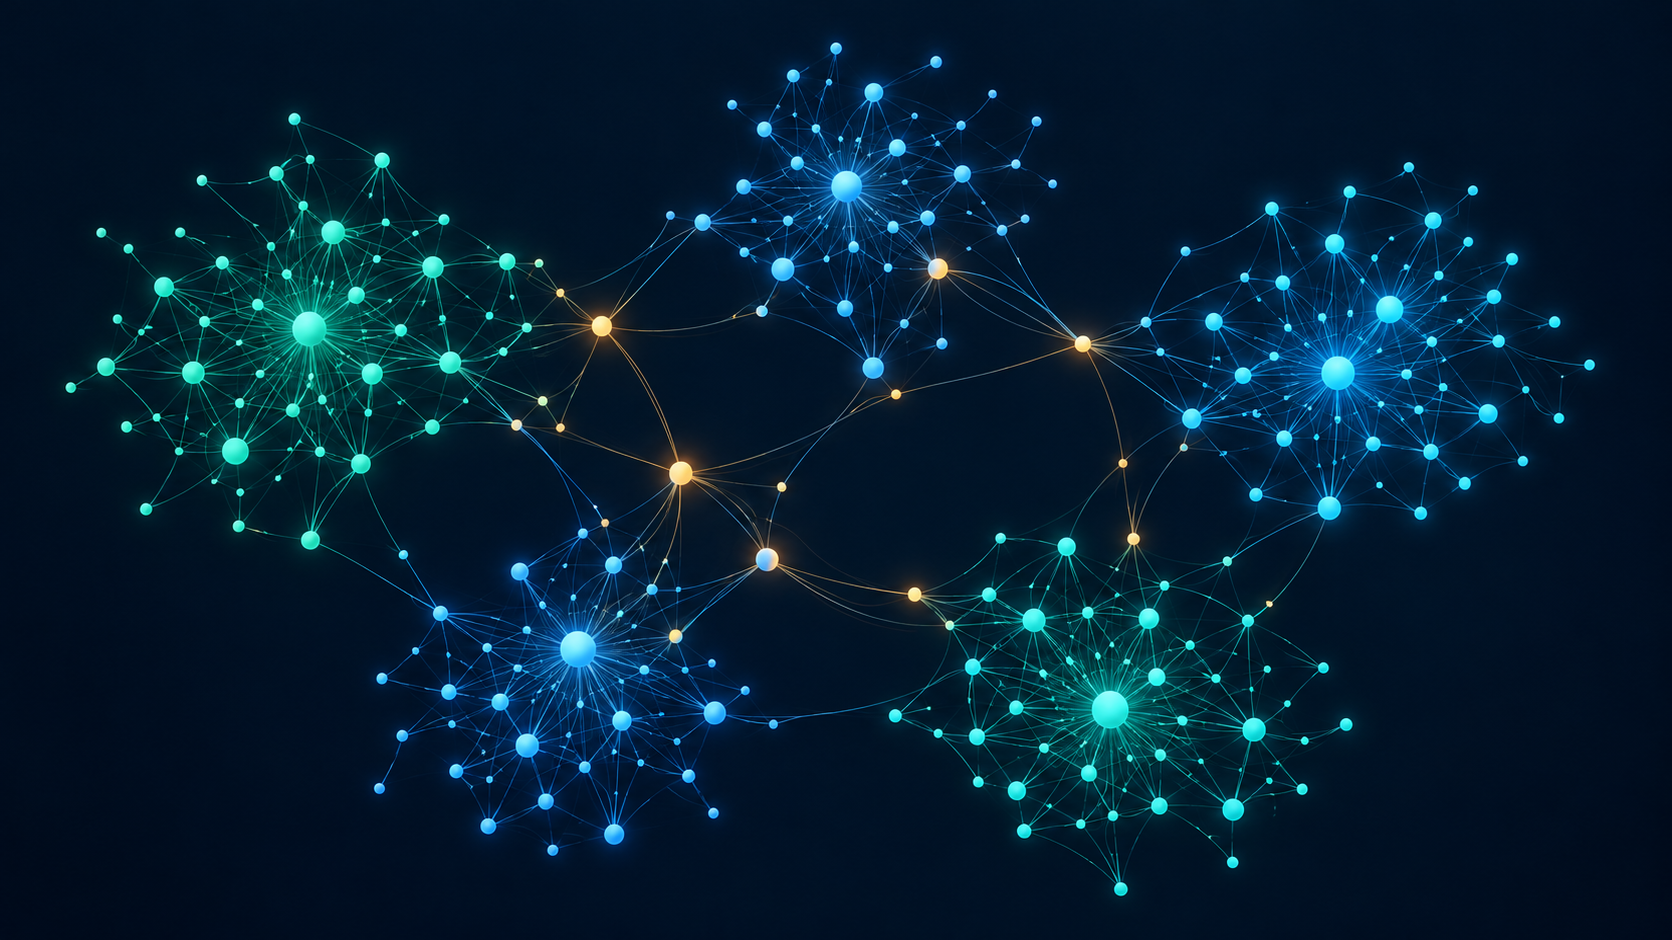
Illustrative representation of an eepsite relationship graph

Illustrative representation of an eepsite relationship graph, not study data.

A three-study, cross-layer measurement program using a directed multiplex graph framework. Study 1 is complete; Study 2 is underway.

Read about the research →
Latest Investigations

Case files

  • CASE-2026-001 · Aug 2026 · Simulated
    Inside Flare Darkroom
    Initial access brokers to cross-forum intel · 3-part series
  • CASE-2026-003 · Jun 2026 · Simulated
    Solvi Systems
    ICS supply-chain intrusion · 8 ATT&CK techniques
  • CASE-2026-002 · Jun 2026 · Simulated
    Inside Encryptodera
    Insider threat to AD ransomware · 8 ATT&CK techniques
All investigations →

What I Do

Three areas, one method: collect, pivot, map, write it up.

Anonymity-network research

Measuring how I2P hidden services link, churn and cluster, using crawling and graph analysis that others can reproduce.

Research →

Threat investigations & CTI

Working intrusion scenarios end to end: scoping, IOC pivoting, timeline reconstruction and ATT&CK mapping, written as finished reports.

Case files →

Threat hunting & detection

KQL and Splunk hunting from SOC work, and a detection-engineering study turning investigation findings into tested rules.

Background →

Now

Updated Oct 2026
  • I2P Study 2: eepsite churn and link-graph changeIn progress
  • Valdoria Votes, Part 2Writing
  • Practical Detection Engineering studyStudying

About me

Joshua Berkoh

SOC analyst turned researcher. I started in incident triage, did security engineering, and now study how anonymous networks are structured.

  • 2024 –PhD researcher, University of Cincinnati
  • 2023Security Engineer Intern
  • 2021 – 22SOC Analyst, Virtual Infosec Africa
More about me →

Hiring

Hiring for CTI, threat hunting or security research?

I’m open to internships and full-time roles. Email is the fastest way to reach me.